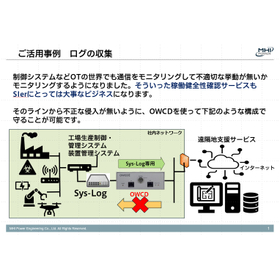
Preventing the use of syslog collection circuits by malware: A prerequisite for SOC collaboration.
SOC services must absolutely not be a pathway for malware intrusion. The number of case studies adopting malware countermeasures is steadily increasing.
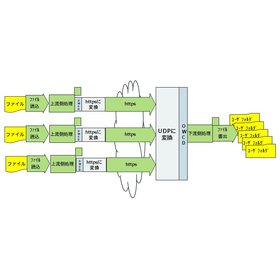
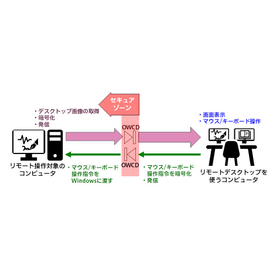
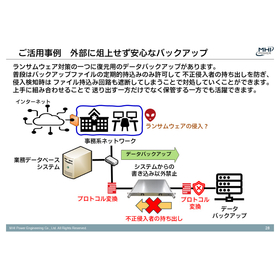
EDR = "micro monitoring" of terminals, SIEM = "macro monitoring" of the entire organization, and SOC = a "team of people (command center)" that monitors, analyzes, and responds 24/365 using those tools. The issue is the "people" who monitor, analyze, and respond 24/365. To achieve zero trust, it is essential to continuously collect and analyze logs and monitoring data from each device, but if the information for system management cannot be sent to infrastructure engineers, it becomes hopeless to conduct detailed analysis. Therefore, it is a natural progression to outsource to external specialized services. However, there is no difference in connecting to external services, and the question remains on how to implement intrusion prevention. If an intrusion occurs from here, it could lead to catastrophic consequences... This is where the data diode "OWCD," which can restrict data transmission to one direction only, comes into play! OWCD is perfect for collecting mirroring data sent to external SOC specialized services and for sending logs from OT to SIEM. The adoption by infrastructure engineers is rapidly increasing. It has become indispensable for support services. To all SIers, if you want to promote cybersecurity, let's effectively utilize boundary control as well. There is an explanatory video linked below! Feel free to contact us.
- Company:MHIパワーエンジニアリング 高砂事業部
- Price:1 million yen-5 million yen